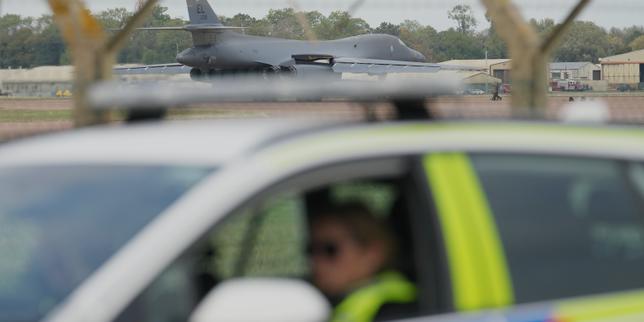
Every time a suspicious package goes missing, a drone loiters near a perimeter fence, or a low-level cutout gets collared outside a sensitive installation, the playbook writes itself. Whitehall holds a hurried briefing, Downing Street leaks strong indications of state-backed meddling, and the headline locks onto Tehran before the ink on the police report has even dried. It is neat. It is convenient. And it is strategically bankrupt.
I have spent years watching intelligence assessments turn into political blunt instruments. When the British Prime Minister steps up to announce heavy intelligence pointing toward Iranian fingerprints on a botched plot against a military base, the reaction from the commentariat is entirely predictable: hand-wringing about escalation, warnings of cyber retaliation, and recycled think-tank chatter about proxy networks. Everyone nods along to the consensus because blaming a perennial bogeyman requires zero heavy lifting. Also making headlines in related news: Why California Partisan Redistricting Changes Everything for National Power.
Let us stop pretending this knee-jerk attribution represents serious security analysis. It is an administrative comfort blanket designed to mask a much messier, far more uncomfortable reality: Western military infrastructure is porous, privatized, and chronically vulnerable to opportunistic actors who do not need direct orders from the Islamic Revolutionary Guard Corps to cause chaos.
The Convenience Of The Foreign Threat Matrix
When a security breach occurs at a critical facility, institutional self-preservation kicks in immediately. If you admit that a disaffected local contractor bypassed outdated biometric gates with a cloned badge bought on an encrypted forum, you have to fire half your security directorate and overhaul procurement protocols that cost millions. If you blame a sophisticated foreign intelligence apparatus, however, you elevate an ordinary failure of basic operational hygiene into an existential geopolitical struggle. More insights on this are covered by NPR.
Governments love external enemies because external enemies justify budgets. They shift the spotlight away from decaying physical defenses, outsourced security guards earning minimum wage, and chronic underinvestment in counter-intelligence counter-measures at home.
Consider the mechanics of modern sabotage. The intelligence community treats every incident as a monolithic state operation, operating under a Cold War template that no longer applies. We are living through the Uber-ization of espionage. Today, you do not need a deep-cover operative trained in a compound outside Isfahan to surveil an RAF station. You hire a couple of desperate career criminals via Telegram to take blurry photos of a perimeter fence for a few hundred pounds in cryptocurrency.
The distinction matters. When a government frames a low-level mercenary operation as a direct act of state aggression by Iran, it backs itself into an escalatory corner. You cannot sanction a decentralized network of bored teenagers and freelance fixers the way you sanction a central bank. By inflating opportunistic, cash-for-service freelance thuggery into high-stakes statecraft, policymakers misdiagnose the threat entirely.
The Broken Logic Of Deterrence In The Gray Zone
For decades, the West's primary security doctrine rested on deterrence: if you hit us, we hit you harder. But deterrence only works against rational actors who care about preserving assets they actually own.
When applied to modern gray-zone tactics, standard deterrence is completely useless. If an adversary can plausible-deniability its way through a botched reconnaissance mission using disposable local assets, traditional retaliatory threats bounce right off. Threatening massive economic sanctions against a country already living under the heaviest sanctions regime in global history is like threatening to throw a drowning man into a swimming pool. It does nothing.
Worse, this obsession with top-down state attribution blinds security forces to domestic vulnerabilities. I have walked the perimeter of sensitive defense sites across Europe and the UK that look like medieval castles with open drawbridges. Unvetted delivery drivers idle outside munitions stores. Outdated analog CCTV cameras suffer from dead zones that would make a burglar blush. Cyber networks running critical logistics are patched together with legacy software that hasn't seen an update since the coalition government.
Yet, when something goes wrong, the immediate press release points the finger across the Middle East. It is a brilliant diversionary tactic, but it leaves the back door wide open.
The Real Threat Is At The Turnstile
Fixing this requires ditching the geopolitical theater and looking inward at the mundane, unglamorous mechanics of site security.
Stop worrying about whether a middle-ranking officer in the Quds Force signed off on a reconnaissance run in Suffolk. Start worrying about the fact that your entire supply chain relies on sub-contracted logistics firms that sub-contract out to drivers whose background checks consist of a single Google search and a handshake.
The security apparatus must pivot from high-altitude threat attribution to radical operational hardening. That means treating every physical asset as if it is already compromised from within. It means zero trust architecture applied to concrete and barbed wire, not just software servers.
Until the defense establishment stops using foreign adversaries as an excuse for sloppiness at home, these incidents will keep happening. Iran didn't need to infiltrate that base. We left the keys under the mat.