Security is only ever as strong as the human carrying it. When a massive digital asset breach drains billions in a matter of minutes, people usually picture high-end Hollywood hacking scenarios, complex math breaks, or sophisticated code injection. Reality is much messier. Sometimes, the key to unlocking a multi-billion-dollar vault starts with one ordinary laptop sitting on a developer's desk.
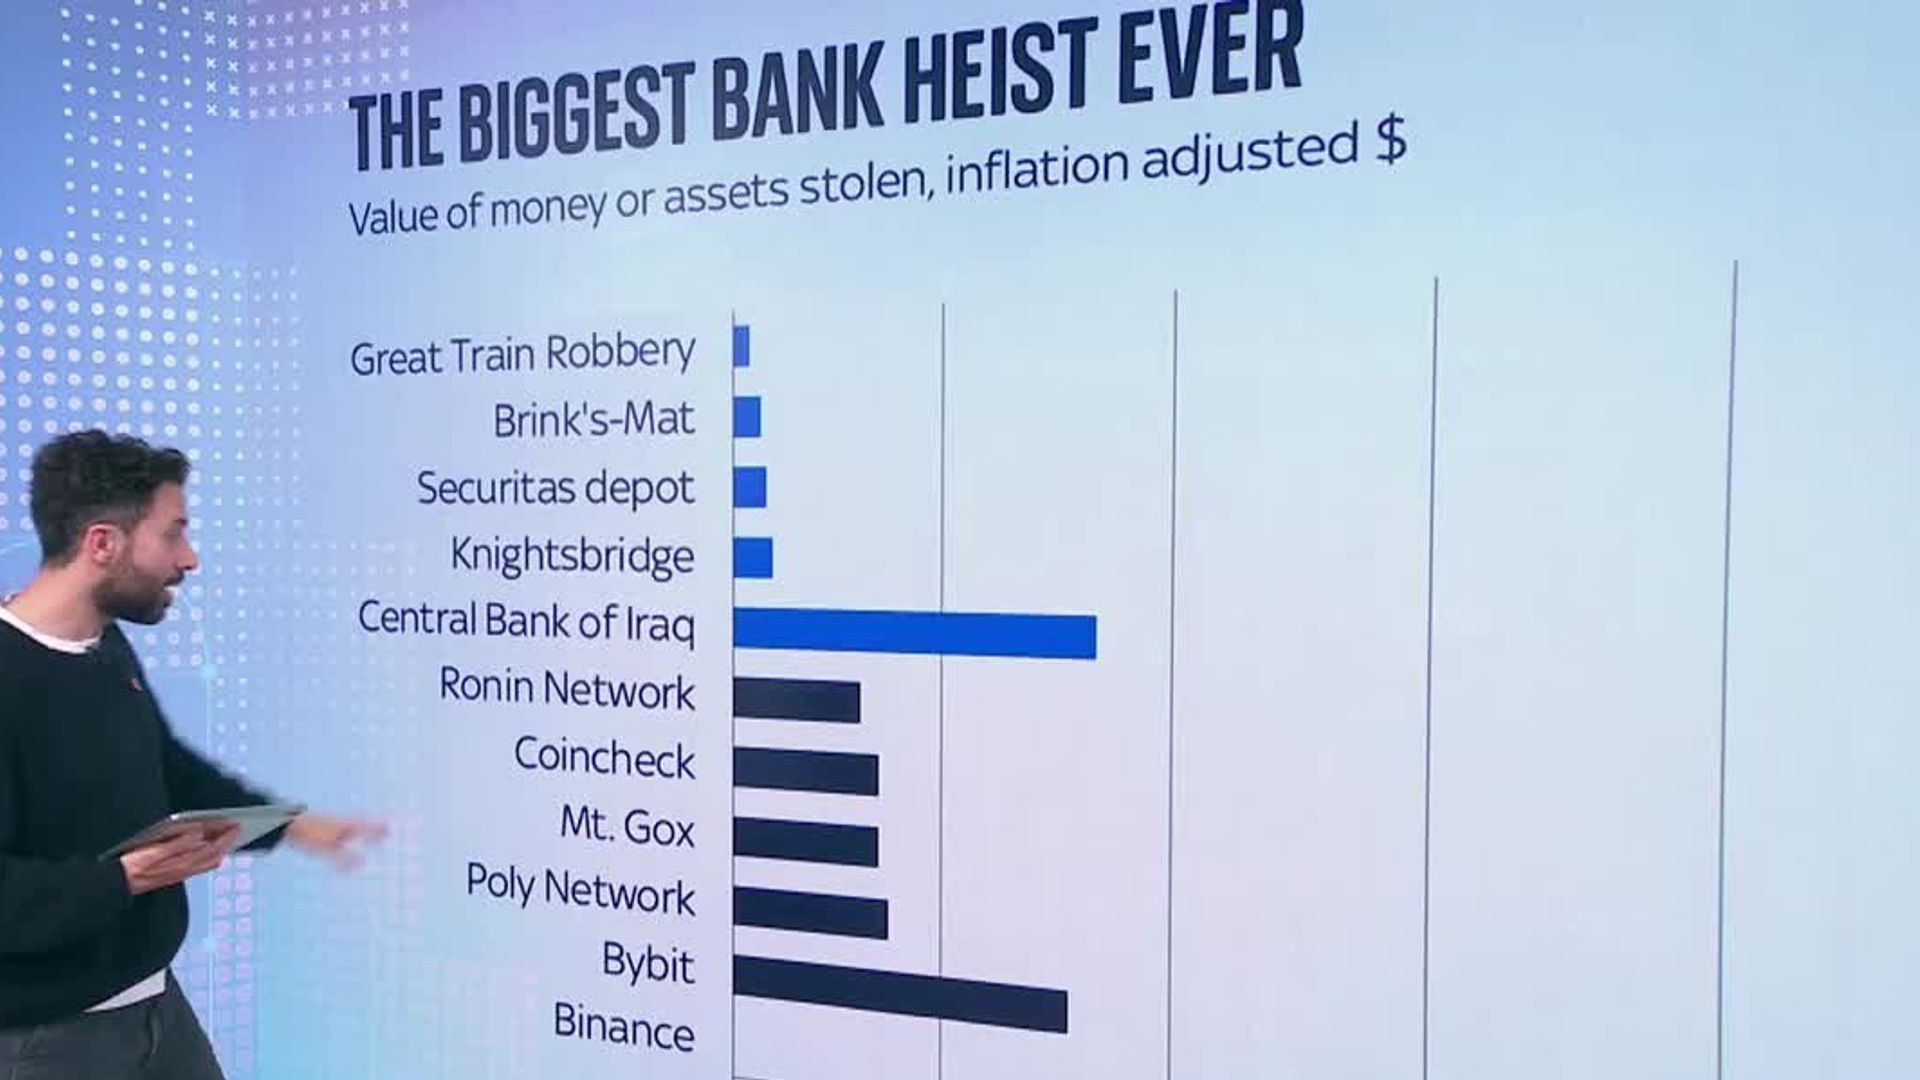
The October 2026 security breach stunned the financial world by siphoning roughly $6.3 billion across multiple blockchains in less than twenty minutes. Investigators and blockchain intelligence firms quickly pointed fingers at state-sponsored actors, specifically tying elements of the attack to groups like TraderTraitor. Yet, the initial vulnerability point highlighted an uncomfortable truth about modern infrastructure: an engineer's compromised laptop.
The Anatomy of a High-Stakes Endpoint Failure
How does a local machine become the gateway to a multi-billion-dollar treasury? Software engineers and core protocol maintainers carry immense cryptographic privileges. They need access keys, deployment tokens, and administrative credentials to push updates and manage hot wallets.
If an attacker manages to slip malware onto a developer workstation through a phishing vector, a malicious dependency, or an unpatched zero-day browser exploit, they inherit those permissions. They don't need to break the blockchain's underlying cryptography. They simply log in through the front door using stolen credentials, masquerading as authorized personnel until the damage is done.
In the wake of the incident, post-mortem reports detailed how rapid coordination between stablecoin issuers like Tether and Circle helped freeze nearly $3 billion of the stolen funds almost immediately. That quick response saved the ecosystem from total chaos. Even so, the sheer speed of the automated withdrawals exposed the fragility of hot wallet architectures that rely on centralized administrative keys.
Why Perimeter Defense Fails Developers
Tech companies spend millions on firewalls, intrusion detection systems, and zero-trust network architectures. They lock down data centers behind biometric gates and multi-factor authentication walls. But they often miss the endpoint reality.
Developers work across diverse environments. They clone repositories from open-source registries, test scripts on local virtual machines, and connect to public Wi-Fi networks while traveling. Every single one of these actions introduces surface area.
When you prioritize engineering velocity over restrictive security constraints, convenience wins. Engineers want seamless workflows. They want to compile code quickly, push commits without friction, and bypass annoying security prompts. Unfortunately, attackers exploit that exact desire for speed. A single malicious package hidden inside an open-source library can compromise a developer's environment within seconds, quietly harvesting session cookies and SSH keys while code builds in the background.
Fixing the Developer Security Gap
Protecting against endpoint-driven breaches requires shifting how organizations view internal trust. You cannot treat an employee's laptop as a trusted zone just because an authorized user logged into it.
Hardware security keys and isolated execution environments are no longer optional extras. If critical deployment credentials live on a standard operating system where daily web browsing and chat apps run, disaster is only a matter of time. Modern engineering teams must adopt strict isolation protocols, ensuring that production keys never touch a general-purpose developer workstation. Hardware-enforced signing and ephemeral credentials must replace static API tokens that remain valid for hours or days.
Security is a continuous practice, not a checklist item checked off during annual compliance audits. Until organizations treat every single developer laptop as a high-value target that attackers are actively trying to compromise, massive breaches will continue to catch the industry off guard.
How engineer's laptop led to crypto heist
This video provides an in-depth breakdown of how the security breach unfolded and the mechanics behind the compromised engineering infrastructure.